Creepy Data Usage
I recently had a Birthday. Along with that comes birthday cards from loved ones, a stream of facebook well wishes, cards, texts and even a few phone calls.
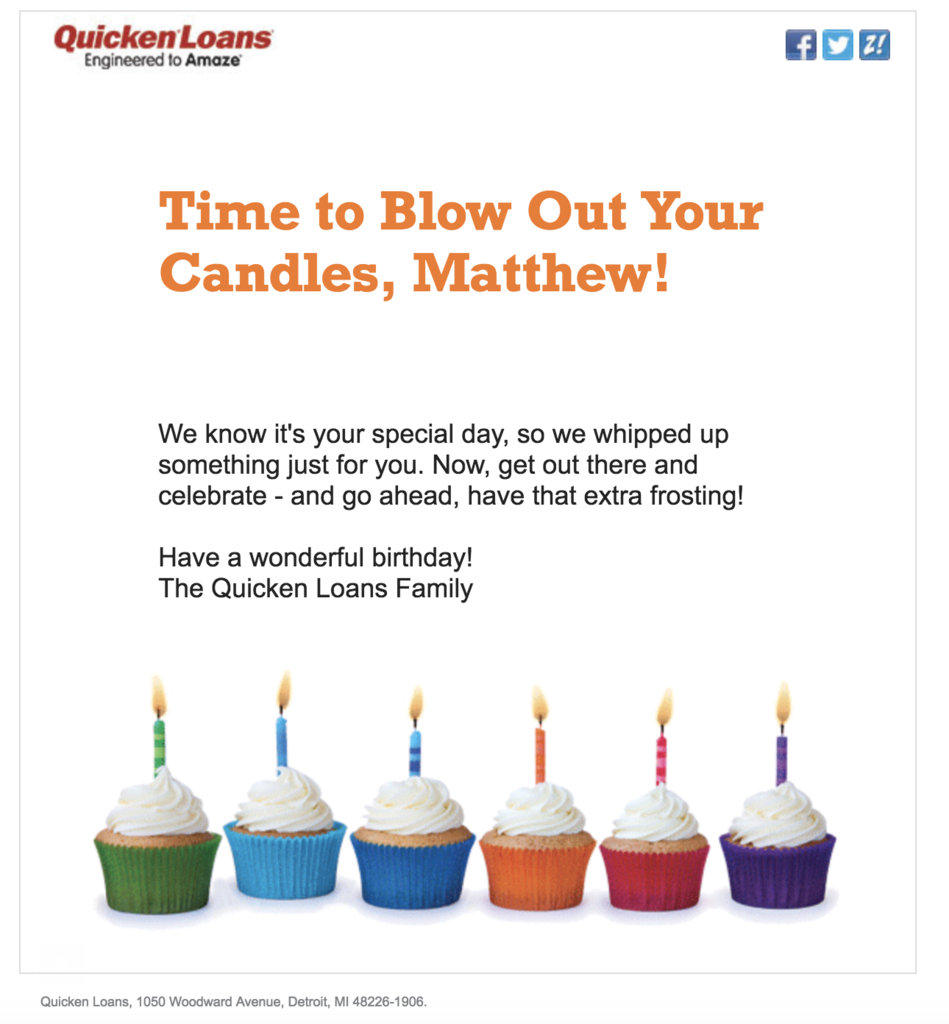
One of the emails I found especially creepy was from Quicken. When we were looking to move maybe 4 years ago, we spoke to Quicken Loans. We didn’t use them for anything besides and inquiry and confirmation that they have great margins on their loan products (ie: way expensive).
Something must have changed in my spam filter because the email got through to me, a rarity, but it does happen.
I opened the email and felt annoyed and like I wanted to move to the EU so I could have Intuit remove my data under GDPR regulations. Here’s why I felt that way.
- Quicken must have stored my data from 4 years ago
- Cross referenced it with their marketing department.
- Felt they knew me well enough to reach out to me on my birthday and that I wouldn’t be smart enough to remember how I gave them my info.
The question becomes… when does it cross the creepy line?
This changes for all people, but ask 5 people using a scenario.
ie: If you applied for a mortgage or credit card 4 years ago, is it creepy to send a BDay card?
Can we publish security footage of our customers?
Can we send you a serving spoon if you visit our cooking class?
Would it be too much if I did this is the basic question. Like Yelp ratings, take the average of 5 - 10 comments and you probably have elements of truth in there.